Software and cloud security engineering brings together the practices that protect applications, infrastructure, data, and users. This guide collects articles on risk management, secure development, identity and access, cloud operations, connected systems, and newer challenges involving AI and GPU workloads.
The guide is organised from fundamentals to advanced topics, so engineers and tech leads can start with broad security practices and then explore specific technologies and risks. It is updated as new articles are published, helping readers find relevant guidance as the collection grows.
Start with these
- Top Cybersecurity Strategies You Must Know Today! – Reviews MFA, timely software updates, and employee training as ways to reduce cyberattack and data-breach risks.
- DevSecOps: Building Secure and Reliable Software at Speed – Describes how DevSecOps integrates security testing, code analysis, automation, and continuous feedback.
- Cloud Security Best Practices for Software Development – Recommends cloud data encryption, least-privilege access, MFA, and tested backups.
What this guide covers
- Security Fundamentals and Risk
- Secure Software and Web Services
- Identity, Access, and Data Protection
- Cloud, IoT, and Resilience
- AI and GPU Security
Security Fundamentals and Risk
Start with common security risks, organizational controls, and ways to assess, mitigate, and respond to threats.
- Top Cybersecurity Strategies You Must Know Today! – Reviews MFA, timely software updates, and employee training as ways to reduce cyberattack and data-breach risks.
- Enhancing Cybersecurity: The Importance of Penetration Testing – Explains how scoped, authorized penetration tests identify weaknesses and verify remediation.
- Penetration Testing: Ensuring the Security of Your Organization – Explains penetration testing basics: define scope, obtain authorization, identify weaknesses, and retest after fixes.
- Automated Risk Mitigation: How to Protect Your Business – Explains how analytics and real-time monitoring can help detect business threats and guide mitigation.
- IT Risk Management: Implementing and Monitoring Controls – Covers IT resilience through risk assessments, access controls, backups, and regular control reviews.
- Robust Risk Management Plan for IT Leaders: A Comprehensive Guide – Outlines IT risk management practices including assessments, incident reviews, access controls, backups, patching, and monitoring.
- DDoS Attack Defense: Mitigation Techniques and Strategies – Explains DDoS disruption and mitigation options such as traffic filtering and cloud-based protection.
- Understanding DDoS Attacks: Types, Methods, and Impact – Describes DDoS impacts and mitigation approaches including traffic filtering and rate limiting.
- Social Media and IT: Benefits, Risks, and Complexities – Explores social media’s benefits for collaboration and its privacy, cybersecurity, and misinformation concerns.
Secure Software and Web Services
Explore secure application practices, software delivery processes, vulnerability mitigation, and web-service design.
- 17 Essential Steps to Fortify Your AI Application – Outlines AI application protections including encryption, role-based controls, input validation, and monitoring.
- AI Application Security: 17 Essential Steps Explained – Outlines AI application protections including encryption, role-based access, input validation, and monitoring.
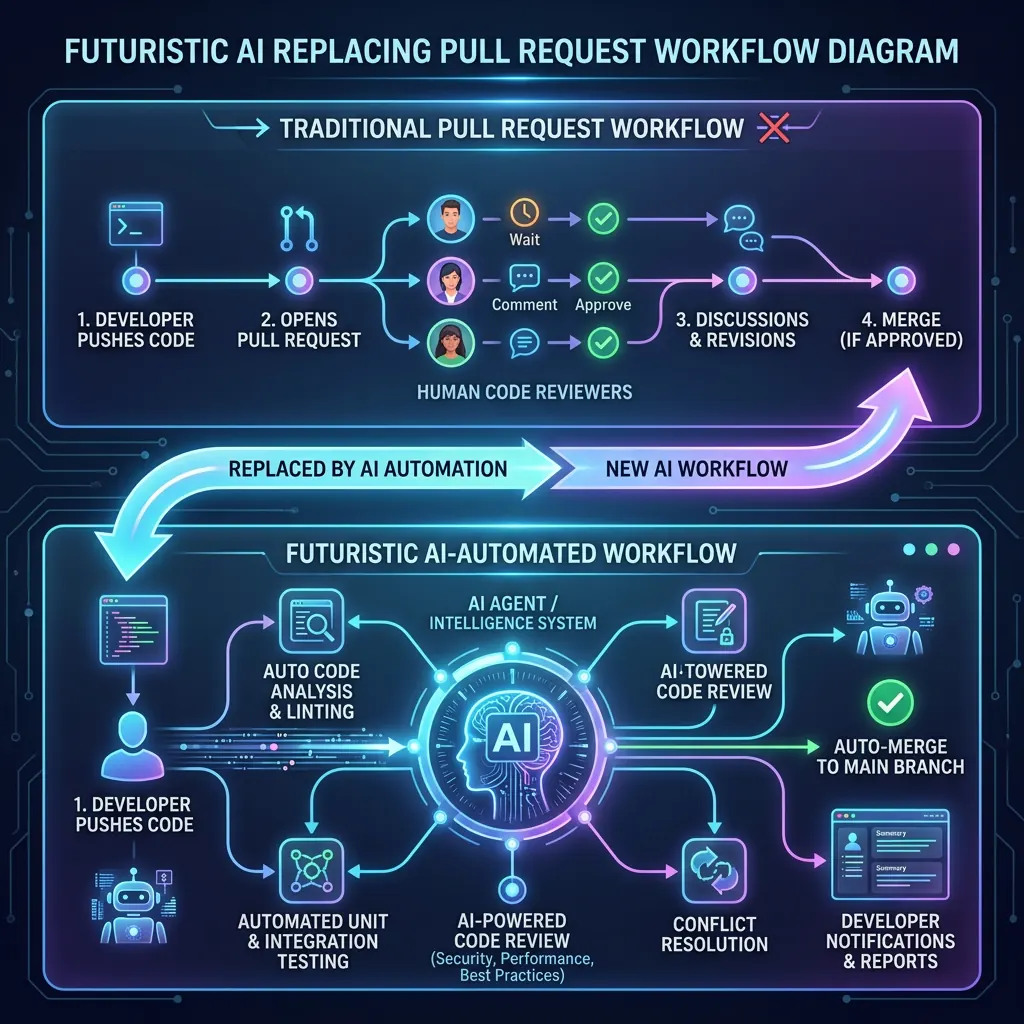
- DevSecOps: Building Secure and Reliable Software at Speed – Describes how DevSecOps integrates security testing, code analysis, automation, and continuous feedback.
- DevSecOps Guide: History, Principles, and Best Practices – Explains DevSecOps principles such as security as code, automated testing, and continuous collaboration.
- Effective Software Vulnerability Mitigation Strategies Explained – Recommends parameterized queries, regular patching, and risk-based remediation to reduce vulnerability risks.
- RESTful Web Services: Design, Security, Caching, and Performance – Reviews RESTful service design using resource URIs, HTTP verbs, caching headers, and clear status codes.
- Web Service Architecture: Scalable, Secure, Reliable Design – Covers scalable web-service design with caching, statelessness, redundancy, monitoring, and automated testing.
Identity, Access, and Data Protection
Review authentication, authorization, least privilege, token validation, and controls for protecting sensitive data.
- Securing Your React Router Application with Auth0 – Shows how to configure Auth0Provider, protect React Router routes, apply roles, and manage token expiry.
- Auth0 in ReactJS: Secure Authentication and Authorization – Explains Auth0 integration in ReactJS, including provider setup, login and logout, and protected routes.
- Guide to Implementing Auth0 in a ReactJS Web App – Covers installing the Auth0 SDK, configuring a React provider, and adding authentication and protected routes.
- A Comprehensive Guide to Securing Microservices with OAuth 2.0 – Covers OAuth 2.0 token validation, scopes, and HTTPS/TLS for securing microservices.
- Step-by-Step Guide to Securing Microservices with OAuth 2.0 – Shows how to secure microservices with OAuth 2.0 scopes, token checks, permissions, and HTTPS/TLS.
- AWS Zero Trust Security: Principles and Best Practices – Reviews AWS Zero Trust practices including MFA, least-privilege IAM, segmentation, and monitoring.
- Implementing Zero Trust Security in an AWS Environment – Explains AWS Zero Trust measures such as MFA, least-privilege IAM policies, and continuous monitoring.
- Mastering AWS IAM: Key Concepts, Features, and Best Practices – Covers AWS IAM least privilege, roles, MFA, and CloudTrail monitoring.
- AWS Identity and Access Management (IAM): An In-Depth Guide – Explains AWS IAM practices including least privilege, MFA, service roles, and CloudTrail monitoring.
- Database Security: Essential Tips to Keep Your Data Safe – Covers database protection through MFA, access controls, encryption, backups, and security audits.
Cloud, IoT, and Resilience
Apply security and resilience practices to cloud services, healthcare systems, IoT networks, and multi-cloud operations.
- Cloud Security Best Practices for Software Development – Recommends cloud data encryption, least-privilege access, MFA, and tested backups.
- Robust Security Measures for Cloud Computing – Covers cloud security measures including encryption, MFA, least-privilege access, and disaster recovery backups.
- Azure Healthcare Solutions: Security, Scalability, and Compliance – Describes Azure healthcare compliance support and scaling containerized applications with AKS.
- IoT Architecture, Protocols, and Security Explained – Compares MQTT and CoAP and reviews IoT encryption, authentication, and patch management.
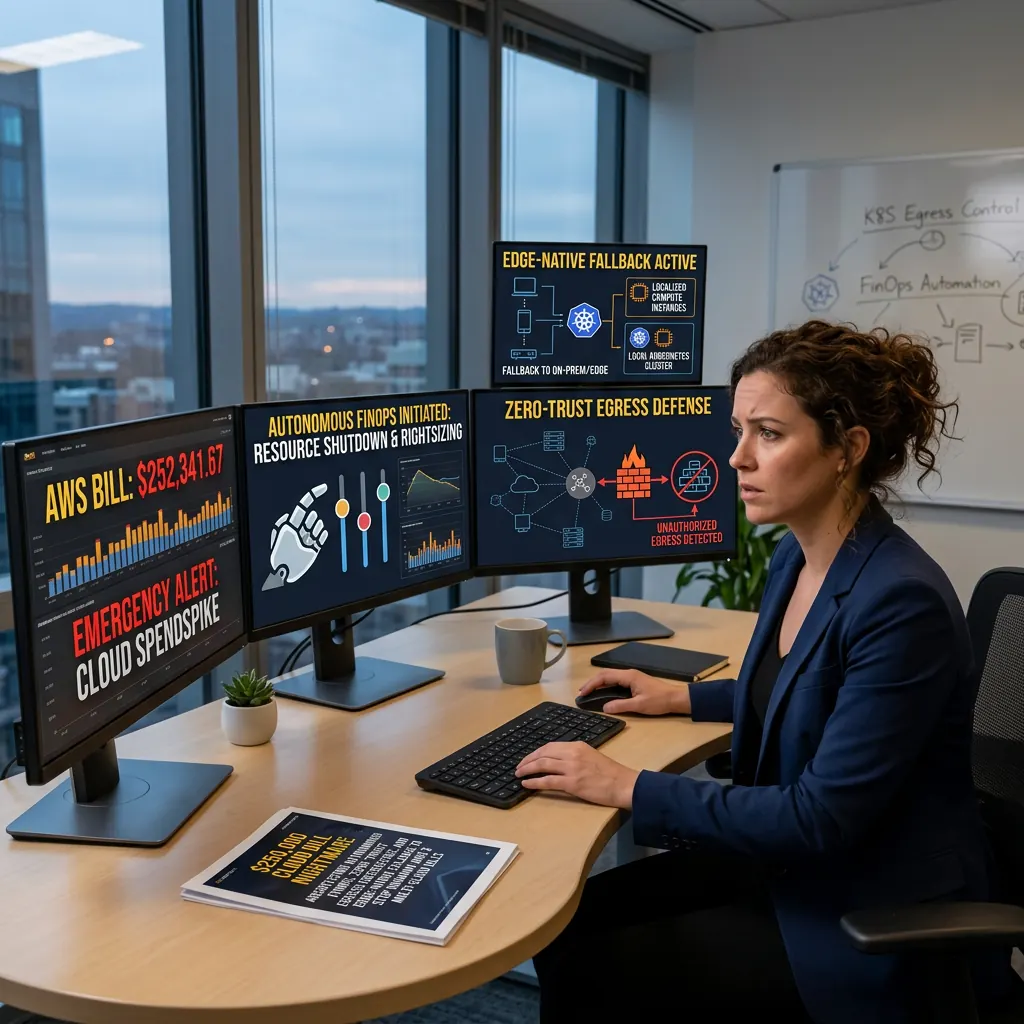
- Cloud FinOps, Zero-Trust Egress, and Edge Fallback – Covers eBPF egress monitoring and budget-aware S3 circuit breakers for runaway serverless workloads.
- eBPF Zero-Trust Egress and Multi-Cloud Failover – Explains eBPF egress controls and circuit breakers to support multi-cloud failover during silent outages.
- Healthcare IT Standards, Compliance, and Security in Practice – Covers healthcare IT risks and controls including assessments, access restrictions, encryption, and incident response.
- Healthcare Information Security: Compliance and IT Standards – Reviews healthcare information security practices for protecting patient data and meeting regulatory requirements.
AI and GPU Security
Consider AI-specific risks and advanced protections for GPU memory, tenant isolation, and agentic workloads.
- Zero-Trust GPU Memory Fabrics for Agentic State – Explains how paged attention and asynchronous memory tiering can reduce GPU VRAM pressure and preserve agent state.
- eBPF Security Against Prompt Jailbreaks in GPU Enclaves – Describes eBPF syscall monitoring, tenant isolation, and confidential-computing enclaves for GPU memory security.
- AI Unleashed: Revolutionizing Cybersecurity with Smart Defense – Covers AI-supported anomaly detection, incident response, and user-behavior monitoring for cybersecurity.
- AI Cybersecurity: Proactive Defense – Describes AI-enabled anomaly detection, automated response, and continuous monitoring for security teams.
- Navigating AI Security Challenges: A Comprehensive Guide – Surveys AI security concerns including cyberattacks, privacy, bias, encryption, anonymization, and ethical safeguards.
- AI Security: Navigating Risks and Ethical Considerations – Covers AI risks such as data breaches, adversarial attacks, and bias, alongside access and mitigation measures.
Frequently asked questions
What are the first steps in improving software security?
Start by identifying the systems, data, and users that need protection, then assess likely risks and existing controls. Apply foundational measures such as strong authentication, least-privilege access, secure input handling, timely patching, and tested backups. Build security checks into development and revisit them as the application and its threats change.
How does zero trust apply to cloud environments?
Zero trust treats access as something to verify rather than assume based on network location. In practice, teams can authenticate users and services, grant only the permissions needed, segment workloads, and monitor activity. Controls should be applied consistently across cloud resources and reviewed when systems, identities, or business requirements change.
How can teams make security part of software delivery?
Teams can integrate security into planning, coding, testing, deployment, and operations instead of relying only on a final review. Automate repeatable checks, review dependencies and code changes, and define a process for prioritizing and fixing findings. Clear ownership and feedback between development and security teams help keep controls practical and maintainable.
Keep learning
Explore the other software engineering guides, or subscribe for free to get new articles in this guide by email.